Nexus PRO compared differently

What happens after an ordinary security tool says “request blocked”?

The useful comparison is not who has the longest checklist. It is whether your security can protect availability, reveal hostile intent, learn safely and explain the result.

WordfenceSucuriPatchstackMalCareSolid Security
The Nexus question

Was the request malicious—or was the workload dangerous?

A valid WooCommerce request can still consume enough PHP and database work to damage availability. A shared public IP can still represent many unrelated customers. A firewall decision can still need local WordPress context. Nexus PRO was built around those harder cases as well as conventional security signals.

Where Nexus goes further

Seven questions to ask before choosing a WordPress security stack.

Each scenario focuses on a real outcome in the current Nexus PRO platform.

02
Shared networks

What if one IP represents hundreds of real customers?

Mobile carriers, offices, hotels and CGNAT can place unrelated visitors behind one public address. Nexus can combine network pressure with client continuity and behavior before escalating protection.

IP pressure ≠ human identity.
03
Beyond virtual patching

What protects the site when there is no vulnerability to patch?

Virtual patching solves an important class of exploit problems. It does not make every availability threat a vulnerability. Nexus also addresses abusive crawling, authentication pressure, commerce-state abuse and resource exhaustion.

No CVE required.
04
Application context

What happens after traffic reaches WordPress?

Nexus runs with local WordPress and WooCommerce context. Protection can account for application state, authentication, resource pressure, integrity signals and the security surface actually exposed by the site.

Perimeter filtering is not the whole story.
05
Evidence & correlation

Do ten suspicious events automatically become one attack?

No. Nexus keeps observations separate when the evidence does not justify a relationship. Threat Radar, Incident Replay, Constellation and the Causality Matrix preserve the difference between what was recorded and what can actually be concluded.

Observed ≠ automatically correlated.
07
Validated adaptation

Can the attack strengthen tomorrow’s protection safely?

Adaptive Defense recognizes recurring behavior and evaluates a proposed response before local containment becomes active.

Learn first. Validate before acting.
Named comparison

What Nexus adds when you already know the market leaders.

These are deliberately narrow comparisons. We focus on the additional security problems Nexus is designed to handle, rather than repeating every feature each product already offers.

Wordfence

Rate limits are not resource awareness.

Wordfence publicly documents request/page-view rate limiting and IP-based lockouts. Nexus adds shared-network context and WooCommerce resource-pressure decisions when volume alone is not enough to identify the right response.

See the production WooCommerce case →
Sucuri

The edge cannot be the only point of context.

A cloud WAF makes its decision before the request reaches the origin. Nexus adds request-time context from inside WordPress and WooCommerce, where application state, resource pressure, integrity and local security evidence are available.

Explore application-aware protection →
Patchstack

A vulnerability does not have to exist.

Virtual patches are built around vulnerable software and exploit conditions. Nexus also protects availability when valid-looking automation becomes expensive enough to hurt WordPress or WooCommerce without exploiting a vulnerability.

Explore runtime protection →
MalCare

Bot blocking is not the same as commerce-aware containment.

Nexus is explicitly designed around WooCommerce pressure, expensive commerce surfaces and automated state changes, with continuity-aware decisions tied to what the local store is experiencing.

Explore WooCommerce Defense →
Solid Security

Login hardening is only one part of the pressure story.

Nexus combines login and administrator protection with early resource containment, runtime traffic defense, WooCommerce-aware controls, malware and integrity checks, and evidence-led investigation.

Explore the full defence stack →

Comparison language reflects publicly documented product behavior reviewed in September 2026. Products change over time. Nexus claims on this page describe capabilities already present in the current PRO product line.

Same site. Different security question.

Ellicon.gr was not primarily failing because of an exploit.

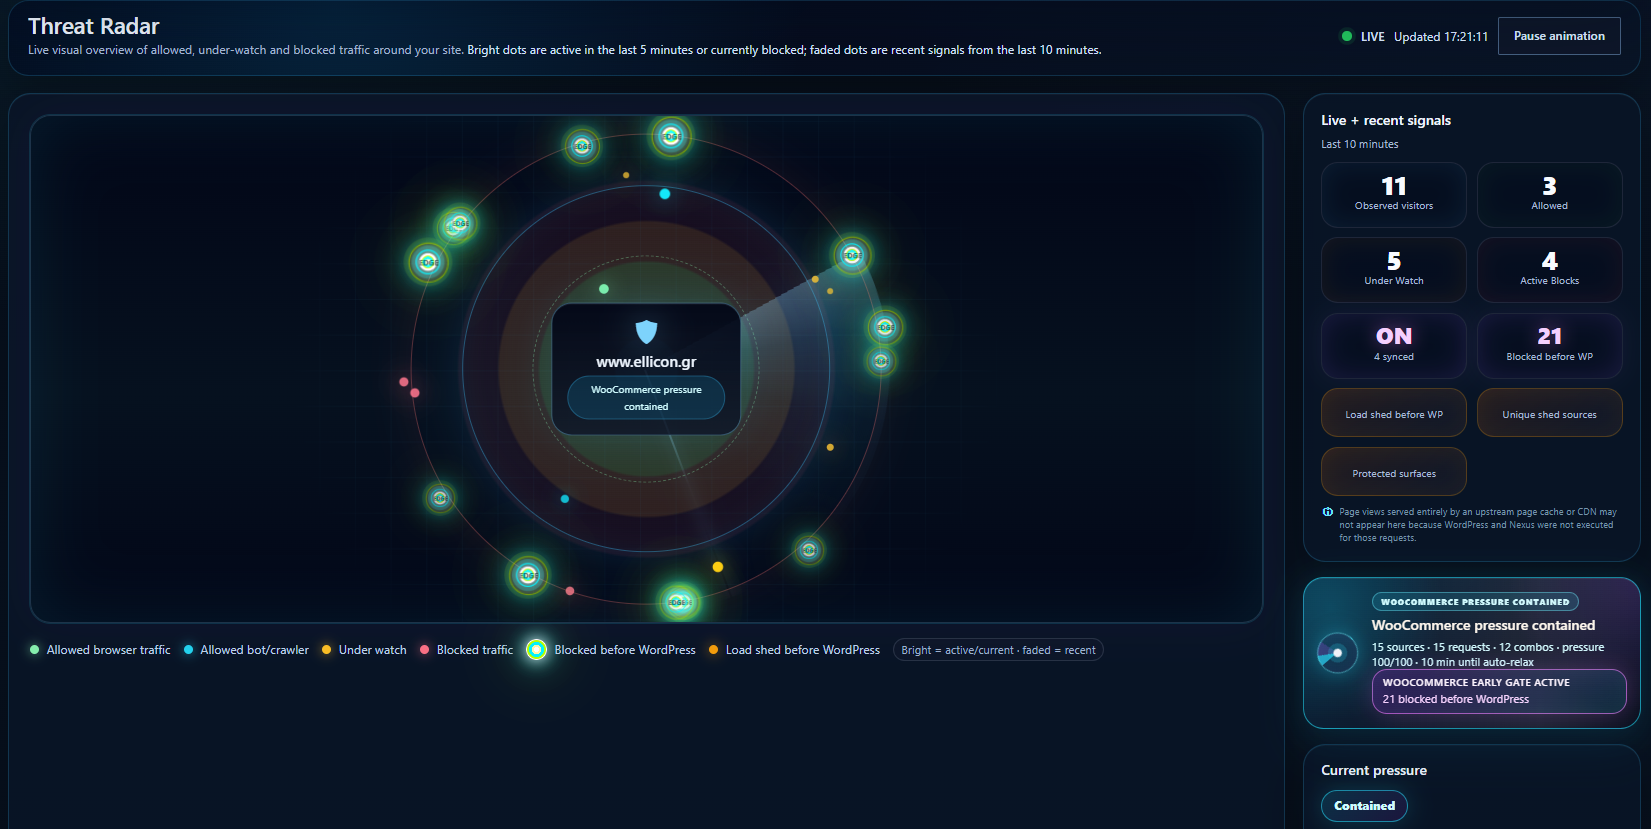
Wordfence Extended Protection was already installed. The recurring availability problem was automated WooCommerce activity that could look like ordinary web requests while forcing expensive application work. Nexus addressed the resource-pressure failure mode directly.

  • Qualifying expensive requests can be contained before full WordPress/WooCommerce execution.
  • Shared-network context reduces the need for blunt source-based assumptions.
  • Commerce state changes can be neutralized without closing the storefront to entire countries.
Read the Ellicon.gr case study
Nexus Threat Radar showing WooCommerce pressure containment on Ellicon.gr
Real production evidenceThreat Radar · Ellicon.gr
Choose by failure mode, not feature count

See what Nexus PRO protects differently.

Full active security for WordPress and WooCommerce from $139/year. VAT included.